Microsoft to block Entra ID script injection attacks by late October 2026
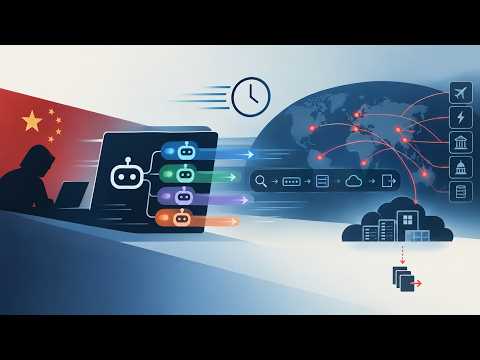
The company will block external script injections during sign-ins by late October 2026 as part of a security initiative triggered by 2023 breaches.
Timeline
- Chinese hackers breached Exchange Online mailboxes
- Service plan names updated to include Entra ID Free, P1, and P2
- Microsoft reveals plans to secure Entra ID sign-ins from script injection
- Enforcement of Content Security Policy to block external script injection begins
- Rollout of script restrictions expected to conclude
Microsoft will begin enforcing a Content Security Policy to block external script injection attacks during Entra ID sign-ins starting mid-October 2026 [3].
The move targets cross-site scripting (XSS) attacks used to steal credentials. This change is part of the Secure Future Initiative (SFI), which was announced after Chinese hackers breached the Exchange Online mailboxes of dozens of organizations and hundreds of individuals in May and June 2023 [3].
Microsoft to Enforce New Sign-In Script Protections
A message center update indicates that Microsoft will restrict scripts during Entra ID authentication to only those from trusted Microsoft content delivery network (CDN) domains [3]. This rollout is expected to conclude by late October 2026 [3].
"Microsoft Entra ID will enhance sign-in security by enforcing a Content Security Policy blocking external script injection starting mid-October 2026," the company said [3]. The company added that this change helps protect users from threats such as XSS by allowing only trusted Microsoft-hosted scripts to run during authentication while blocking unauthorized or externally injected code [3].
Microsoft has warned enterprise customers to stop using browser extensions or tools that inject code into sign-in pages before the deadline [3]. IT administrators are urged to test sign-in flows using browser developer consoles to identify potential dependency issues [3]. Admins can identify impact by looking for violations that appear in red text within the console [3].
Browser-based sign-in experiences using login.microsoftonline.com are the only flows affected; API-based and Microsoft Authentication Library (MSAL) flows are not [3]. Microsoft noted that users will still be able to sign in even if unsupported script injection tools stop functioning, and the change is enabled by default without requiring tenant configuration [3].
The Secure Future Initiative Strategy
These protections are a component of the Secure Future Initiative (SFI) [3]. Microsoft launched the SFI after Chinese hackers breached the Exchange Online mailboxes of hundreds of individuals and dozens of organizations in May and June 2023 [3]. The company first revealed the specific plans to secure Entra ID sign-ins from script injection in a November 2025 announcement [3].
The SFI includes multiple hardening measures beyond script blocking [3]. Microsoft has disabled ActiveX controls in Windows versions of Microsoft 365 and Office 2024 apps [3]. The company also updated security defaults to block legacy authentication protocols for OneDrive, SharePoint, and Office files [3].
The company's defensive posture is informed by the Blue Report 2026, which analyzed defense techniques across 338 million simulations in production environments [3]. This report highlights that while overall prevention scores can be high, prevention drops sharply once attackers possess valid credentials [3].
Risks to Entra ID Tenants
The security updates follow the rebranding of Azure Active Directory to Microsoft Entra ID [8][9]. Microsoft stated the name change reflects a multicloud approach and unifies its identity and network access products, including Permissions Management, Verified ID, and the Security Service Edge (SSE) category [8][9]. Service plan names were updated on October 1, 2023, to include Entra ID Free, P1, and P2 [8].
Despite these product updates, the Microsoft Incident Response team reports frequent cases where organizations lose control of their Entra ID tenants [2]. According to the team, these losses often result from administrative oversight, misconfiguration, exclusions to security policies, or insufficient protection for identities [2].
Securing Entra ID requires different tools and processes than on-premises Active Directory [2]. Failures in the cloud control plane, which serves as the foundation for an organization's entire cloud footprint, can allow attackers to move laterally between hybrid environments, potentially causing business-crippling outages [2].
Supplementary Identity Security Measures
Beyond script blocking, Microsoft provides several tools to reduce identity gaps [5][6]. Small businesses, particularly those with 5 to 30 employees lacking dedicated IT staff, are advised to enable "Security defaults" in Entra ID [6]. This feature, available for the free version of Entra ID, provides basic multi-factor authentication (MFA) via the Microsoft Authenticator app or OATH TOTP-compatible apps at no extra cost [6].
Other available measures include self-service password reset (SSPR), which allows users to reset passwords without administrator intervention [5]. This is designed to reduce help desk load and productivity loss when users are locked out [5]. SSPR utilizes an SMTP relay service operating in active-active mode across several regions to send notifications [5].
For cloud-native workloads, Microsoft Entra Workload ID enables pods in Azure Kubernetes Service (AKS) to authenticate to protected resources, such as Azure Key Vault and Microsoft Graph [4]. This system uses OpenID Connect (OIDC) federation to assign workload identities to pods [4]. On AKS Automatic clusters, this workload identity and the OIDC cluster issuer are preconfigured by default as part of the cluster's security defaults [4].
What we don't know
- Which specific browser extensions are most likely to be broken by the new Content Security Policy?
- Exactly how many organizations were affected by the May and June 2023 Exchange Online breaches?
- How many Entra ID tenants are currently managed with "Security defaults" versus customized conditional access policies?
Sources
- Entra ID Security Assessment - Semperis — semperis.com, Oct 25, 2026
- Microsoft to block Entra ID script injection attacks starting October — bleepingcomputer.com, Oct 24, 2026
- Use a Microsoft Entra Workload ID on Azure Kubernetes Service (AKS) - Azure Kubernetes Service — learn.microsoft.com
- Self-service password reset deep dive - Microsoft Entra ID — learn.microsoft.com
- Microsoft 365 Security Settings | 7 Items Small Businesses Should Do First (Are MFA and Premium Necessary?)|ひとり社長のAI業務自動化 — note.com
- New name for Azure Active Directory - Microsoft Entra — learn.microsoft.com
- Azure AD is being renamed to Microsoft Entra ID | Microsoft Entra Identity Platform — devblogs.microsoft.com
Photos and video from the reports
- Photo: A diagram showing identity protection and secure access for Microsoft Entra ID.
- Video: A diagram of Microsoft Entra ID's unified identity management system.
- Photo: A screenshot of the Microsoft Entra ID apps dashboard.
- Photo: A screenshot of the Identity Protection dashboard in Microsoft Entra.
Further reading
- NIST and CISA finalize token security guidance for federal cloud ...
NIST and CISA have finalized guidance for protecting signed identity and access tokens used in federal cloud systems.