Identity attacks rise 32% as actors shift to bypassing MFA
Threat actors increasingly target session tokens and human behavior to circumvent multi-factor authentication, according to new industry analysis.
Key figures
| Identity-based attacks increase | 32% |
|---|---|
| Identity-based attacks starting as password attacks | More than 97% |
| AiTM attacks increase | 146% |
| Daily AiTM incidents | nearly 40,000 |
| MGM ransomware attack cost | over $100 million |
Timeline
- Google research found MFA thwarted 99% of automated credential attacks
- Top malware strains could steal session cookies
- Lapsus$ group targeted Microsoft, Samsung, and Nvidia
- Uber contractor approved notification after constant prompts
- Attackers impersonated employee to reset Okta MFA
- Identity-based attacks rose 32%
- Largest SaaS breach began with compromised third-party app
- Projection that over 90% of credential compromise attacks involve kits
Identity-based attacks rose 32% in the first half of 2025. Attackers frequently bypassed multi-factor authentication (MFA) by stealing session tokens or exploiting human behavior [3].
MFA protects the point of entry, but it does not secure the subsequent session. As Obsidian Security notes, "MFA protects the authentication moment, not the session that follows" [3].
This gap allows attackers to target session cookies. These are small blocks of data stored in a browser that identify a signed-in user so they do not need to re-authenticate until the session expires or they log out [1].
Password attacks target MFA gaps
More than 97% of identity-based attacks in the first half of 2025 began as large-scale password attacks [3]. Actors used stolen credentials to target MFA-protected accounts [3].
Attackers are no longer attempting to crack the cryptographic mechanisms of MFA. Google research from 2019 found that MFA already thwarted 99% of automated credential-based attacks and 93% of phishing campaigns [1].
Instead, actors search for gaps in session management and human trust [3]. By focusing on the session rather than the login, attackers can enter systems without triggering the second-factor prompts that typically stop automated attacks [3].
Once a user completes MFA, the system issues tokens that prove identity for a set duration. Attackers who steal these post-authentication artifacts bypass the MFA process entirely [3].
Growth of AiTM proxies
Adversary-in-the-Middle (AiTM) attacks increased 146% recently. Microsoft reports nearly 40,000 daily incidents [3].
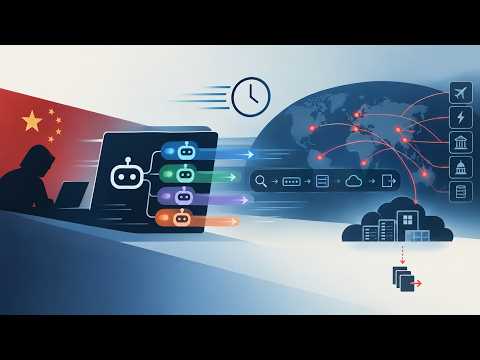
These attacks use transparent HTTP proxies to capture session tokens in real-time during authentication [1, 3]. Because the victim authenticates to the real service through the proxy, the service views the login as successful. This works even against time-based one-time passwords (TOTP) from authenticator apps [3].
Phishing kits now offer these capabilities as a service. Eleven major AiTM kits, including EvilProxy, Tycoon 2FA, Mamba, and Evilginx2, are available as Phishing-as-a-Service platforms [3].
Attackers can rent these platforms for a few hundred pounds per month. Industry projections suggest that most credential compromise attacks will involve these kits by late 2026 [3].
Session theft via malware
Attackers also use specialized malware to harvest session data from devices. Okta reports that infostealer modules—designed to extract session cookies from browsers—are often delivered through malspam or pirated "cracked" games [1].
These modules silently extract cookies for sale on dark web forums, sometimes with tools that mimic the target's browser configuration [1].
This method bypasses MFA because the stolen cookie proves the user has already authenticated [1]. Okta notes that the majority of malware families listed in CISA's Top 10 Malware Strains of 2021 report are capable of stealing session cookies [1].
Social engineering and supply chain exploits
Attackers exploit human psychology through "MFA fatigue." The Lapsus$ group targeted Microsoft, Samsung, and Nvidia in 2022 by sending numerous push notifications and contacting victims claiming to be IT support [3].
On September 15, 2022, an Uber contractor approved a notification after an hour of constant prompts [3].
Social engineering of support staff also enables bypasses. Previously, attackers have impersonated an employee on a call to the Okta help desk to reset MFA. This led to a ransomware attack costing MGM over $100 million [3].
Recent breaches have targeted the supply chain. The largest SaaS breach of 2025 began with a compromised third-party app and the exploitation of Salesloft-Drift OAuth tokens [3].
Obsidian researchers found the blast radius of this attack was 10x greater than previous incidents where attackers infiltrated Salesforce directly [3].
What we don't know
- Which specific third-party app triggered the largest SaaS breach of 2025?
- What specific percentage of the 32% rise in identity attacks was attributed to AiTM proxies versus infostealer malware?
Sources
- Defending against Session Hijacking — Okta Security RSS Feed, Aug 9, 2022
- MFA Bypass: Attack Techniques and Defense Strategies — obsidiansecurity.com, Oct 24, 2026
Photos and video from the reports
Further reading
- How to Detect and Stop Session Hijacking: 12 Steps
A guide detailing 12 steps to detect and stop session hijacking and cookie theft across different identity providers.