Chinese-state aligned actor uses ARTEX AI agent to target identity providers
Security firm Wiz identified Storm-0940 using an autonomous penetration-testing framework to probe Okta, Entra ID, and Cognito across software vendors and financial institutions
Timeline
- Chinese developer publishes ARTEX as an open-source framework
- Wiz identifies Storm-0940 using ARTEX to target software vendors and identity providers
- ARTEX used in attacks against Japanese companies
- Developer makes ARTEX closed-source due to reported abuse
- Reuters reports at least nine banks targeted
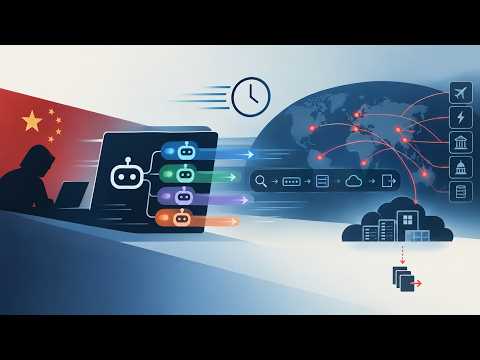
In October 2026, security firm Wiz identified a Chinese-state aligned actor, known as Storm-0940, using an autonomous AI penetration-testing agent called ARTEX to target multiple software vendors and identity providers [2].
The activity demonstrates the use of AI-driven agents to automate the discovery and exploitation of identity infrastructure. By targeting the control planes of cloud access, the actor attempted to gain footholds in software supply chains and financial systems [2].
Storm-0940 deployment of ARTEX AI agent
Wiz reports that the actor's activity focused on identity providers including Okta, Entra ID, and AWS Cognito, alongside the abuse of Microsoft 365 integrations [2]. The tool was used to uncover authentication bypasses, enumerate APIs, and attempt to access customer data within the targeted vendors' environments [2].
These operations overlap with a broader campaign by Storm-0940, a Chinese-state aligned actor previously linked to supply-chain attacks involving stolen vendor credentials [2]. The use of an autonomous agent allows the actor to scale reconnaissance across multiple cloud environments simultaneously [2].
Mechanics of autonomous reconnaissance and adaptation
According to Wiz, the AI agent follows a consistent sequence, beginning by mapping the target application [2]. The tool downloads JavaScript bundles, exposed source maps, runtime configurations, and OpenAPI documentation to discover internal API routes [2].
Once the map is established, the agent probes authentication by manipulating OAuth callbacks, testing unsigned JSON Web Tokens (JWTs), and password-spraying corporate Okta and Entra ID environments [2]. It also targets account recovery endpoints to invoke password resets and username recovery [2].
To evade security measures, the agent adapts to defense mechanisms in real time [1][2]. Wiz and other reports indicate the tool rotates IP addresses and circulates user agents when it encounters blocks or rate-limiting [1][2].
Expansion into East Asian financial and corporate sectors
The deployment of ARTEX extends beyond software vendors. The framework was used in attacks against Japanese companies in October 2026 and South Korean banks starting in late September [2]. Reuters reported on October 9 that at least nine banks had been disclosed or reported as targets [3].
Technical analysis suggests the agent is powered by large language models (LLMs). Security researcher zephel01 stated that the primary model for ARTEX is DeepSeek v4.1-flash, likely accessed via a reseller called xcai[.]pro [3]. Other sessions reportedly utilized GLM-5.3 and Grok 4.6 [3].
Conflicting attributions and actor motivations
While Wiz links the activity to state-aligned Storm-0940 [2], CrowdStrike Intelligence assessed the actor behind the South Korean bank breaches as likely Chinese-speaking and financially motivated [3]. CrowdStrike Intelligence assessed the actor behind the South Korean bank breaches as likely Chinese-speaking and financially motivated, though it held only moderate confidence in this assessment [3].
Evidence of the tool's use emerged partly through attacker error. Researcher zephel01 noted that an attacker's working server was left as an open directory on port 18899, which contained penetration prompts in Chinese and ARTEX settings [3]. According to zephel01, "It is a story where Claude Code session history, ARTEX settings, and Claude's memory files could be read from the outside" [3].
Developer response and tooling status
ARTEX was originally published as an open-source framework by a Chinese developer in July 2026 [2]. The tool gained rapid popularity, winning Baidu's "Agent+" red team challenge in September and reaching more than 12,000 forks on GitHub [2].
Due to the reported abuse of the framework, the developer made the tool closed-source on October 8, 2026 [2]. The original GitHub page has since been deleted [3].
What we don't know
- Did the actor successfully exfiltrate data from the software vendors, or did most attempts fail as Wiz suggests?
- Which specific Japanese companies were targeted in October?
- Are other LLMs besides DeepSeek, GLM, and Grok being used with ARTEX in the wild?
Sources
- Wiz Details ARTEX AI Attack Activity Targeting Software Vendors and ... — windowsforum.com, Oct 24, 2026
- ARTEX in the Wild: Storm-0940 Expands Targeting of IT and Software Vendors | Wiz Blog — wiz.io
- The South Korean bank breach was not a 'new APT'. The ARTEX working directory was readable from the outside|zephel01 — note.com
Photos and video from the reports
Further reading
- Entra ID / Okta Compromise — IdP Incident Playbook
An incident playbook for containing identity provider takeovers and evicting rogue federation or OAuth persistence.