ThreatDown ITDR correlates endpoint telemetry with identity activity
The tool correlates EDR telemetry with Okta, Entra ID, and Active Directory to trace attacks from initial endpoint compromise to privilege escalation.
ThreatDown Identity Threat Detection & Response (ITDR) correlates endpoint detection and response (EDR) telemetry with identity activity across Active Directory, Entra ID, and Okta to detect credential-based attacks [3].
By unifying signals from these disparate systems, the tool aims to uncover credential threats and reduce the time required for security teams to contain breaches [5].
Correlating EDR Telemetry with Multi-Platform Identity Activity
ThreatDown ITDR monitors identity behavior by correlating user telemetry from EDR with activity across three primary environments: on-premises Active Directory, Microsoft Entra ID, and Okta [4]. The system is designed to natively link these endpoint signals with identity data [4].
This correlation allows security teams to track activity as it moves across different identity platforms [3]. According to product documentation, this approach aims to eliminate blind spots and context switching [3].
Tracing the Attack Chain from Endpoint to Exfiltration
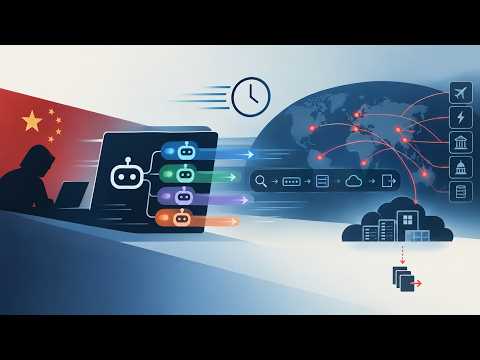
The tool allows security operators to trace the progression of an attack from the initial compromised endpoint through to credential compromise and subsequent privilege escalation [3]. According to product documentation, this mapping provides the full attack story from the compromised endpoint to identity compromise [3][4].
ThreatDown provides guides that illustrate these movements, tracing the path from the first credential attack to attempted data exfiltration [2]. By connecting these dots, the system seeks to show the complete chain of an intrusion without requiring analysts to switch between different security consoles [3].
Accelerating Containment via Unified Signal Monitoring
ThreatDown ITDR integrates identity and endpoint signals into a unified console [5]. This consolidation is intended to help security teams monitor identity behavior more efficiently and accelerate the investigation of potential threats [5].
The objective of this unification is to speed up the containment of credential-based attacks [5]. By providing a single point of observation for both endpoint behavior and identity activity, the tool aims to reduce the overall complexity of security operations [5].
Addressing Complex Federated Identity Environments
ThreatDown ITDR correlates activity across Active Directory, Entra ID, and Okta [3][4]. For example, Microsoft Entra ID can be configured as an external Identity Provider within Okta through federation [1].
In these federated setups, a single compromised identity can potentially grant access across both platforms [1]. ThreatDown ITDR correlates activity across both Entra ID and Okta [3][4].
What we don't know
- What specific EDR telemetry data points are used to trigger the correlation with identity activity?
- Does the ITDR system support identity providers beyond Okta and Microsoft Entra ID?
- How the system handles conflicts or discrepancies between telemetry from different identity providers.
Sources
- One compromised identity. No exploits. Full access. - ThreatDown — threatdown.com, Oct 24, 2026
- PDF TD_ITDR_eBook-v6 - threatdown.com — threatdown.com
- PDF ThreatDown Identity Threat Detection & Response — threatdown.com
- PDF ThreatDown Identity Threat Detection & Response — threatdown.com
- ThreatDown Identity Threat Detection & Response — insight.com
Further reading
- How to Detect and Stop Session Hijacking: 12 Steps
A guide on detecting and stopping session hijacking across Entra ID and Okta using SIEM rules and Python detectors.
- Cloud identity resilience gaps in Okta and Entra ID environments
An analysis of how Okta and Entra ID disruptions can block users and incident responders simultaneously.