Attacker bypasses MFA at 79 organizations using token spraying
An attacker used "token spraying" to bypass MFA at 79 organizations, registering rogue devices and replacing MFA methods to survive password resets.
Key figures
| Organizations compromised | 79 |
|---|---|
| Successful sign-ins | 497 |
| Failed attempts | more than 200,000 |
| Rogue Microsoft Entra ID devices registered | at least 48 |
| Organizations where actor erased MFA methods | 19 |
Timeline
- Start of the campaign compromising Microsoft 365 accounts
- Session used 12 minutes after victim reached MFA prompt
- Session used 4 minutes after victim reached MFA prompt
- End of the campaign compromising Microsoft 365 accounts
An attacker compromised Microsoft 365 accounts at 79 organizations between July 14 and September 22, 2026, by replaying stolen session tokens to bypass multi-factor authentication [1][3].
The campaign shows how attackers can maintain access to corporate environments even after a password reset. By targeting the session tokens issued after a user completes MFA, the actor avoided the need to interact with the authentication process entirely [1][4].
Token spraying campaign hits 79 organizations
The security firm Huntress tracked the campaign, which lasted approximately ten weeks and resulted in 497 successful sign-ins and more than 200,000 failed attempts [1][6]. The actor utilized a technique described as "token spraying," which researchers define as "the same pattern as password spraying, but with stolen tokens instead of guessed passwords" [4]. Unlike traditional password spraying that relies on brute force, token spraying distributes a correct authentication key from the start, rendering defenses designed to detect guessing—such as account lockouts and attempt limits—ineffective [6].
The attacker primarily operated from six IP addresses within the 193.26.115.0/24 range [1][4]. These addresses belong to 1337 Services GmbH, a hosting provider based in Hamburg, Germany [3][4]. The operation was phased, with the attacker moving between addresses in four stages and taking breaks of one to two weeks between them [4][6]. This structure provided weekly-level resilience; Huntress noted that blocking any single address would have stopped only one phase of the attack at most [4][6].
Mechanics of the MFA bypass
The attacker obtained the necessary session tokens through several methods, including social engineering and device-code phishing, where users were tricked into entering a code on Microsoft's legitimate sign-in page [1][3]. They also used adversary-in-the-middle (AiTM) relays, which present a genuine Microsoft login page to the victim and capture the token issued after the user completes the MFA prompt [4][6]. Because the relay passes the real authentication requests as-is, the victim's experience remains perfectly normal, leaving them with no "fake" page to spot [6].
The speed of the exploitation increased over the course of the campaign [4]. In a July 21 case, the gap between a victim reaching the MFA prompt and the attacker using the stolen session from a 1337 Services address was 12 minutes; by September 22, that window had shrunk to four minutes [4][6]. Additionally, Huntress found the actor using a stolen credential for the ConnectWise Cloud Backup (formerly SkyKick) Entra app to pull Microsoft Graph tokens [1].
Researchers identified two distinct replay toolsets. "Build A" used automated OAuth2:Token requests, frequently using a node user agent, against the Device Registration Service, Exchange Online, SharePoint Online, and Microsoft Graph [3]. "Build B" replayed browser sessions through the OfficeHome client and current versions of the Edge or Chrome browsers [3].
Establishing long-term persistence
Once inside an account, the actor took steps to ensure access survived the expiration of the stolen session [3][4]. The attacker registered at least 48 rogue Microsoft Entra ID devices, which followed a naming convention of "DESKTOP-" followed by eight uppercase hexadecimal characters, such as "DESKTOP-54521F46" [1][3]. These devices remain in the directory until manually deleted by an administrator [4].
In 19 of the targeted organizations, the actor erased the victims' existing MFA methods and registered new ones within three hours of the first sign-in [1][4]. In the July 21 case, an authenticator labeled "iPhone 13" was activated on the account less than an hour after the session was hijacked [3][4]. This allowed the attacker to complete MFA for new sign-ins at will [4].
Huntress noted that standard password resets are ineffective against these tactics because they do not remove registered rogue devices or attacker-controlled MFA methods [1][3]. To fully remediate, the firm recommends revoking sessions and resetting passwords, while separately deleting unrecognized MFA methods and devices [1].
Execution of financial fraud
The final stage of the infiltration involved the use of hidden inbox rules to facilitate payment fraud [1]. The attacker created rules with names such as ".", "sss", and "iT" that deleted incoming mail, marked messages as read, or moved them to folders like RSS Feeds and Conversation History [1][4].
These rules specifically targeted emails containing terms related to banking, direct deposits, bonuses, and payroll [4]. In one instance, the attacker sent a payroll-related message to an external accountant and created a rule to hide all subsequent replies from that accountant [4]. In a similar incident, the attacker modified a rule to catch messages mentioning "bank" or "bonus," and created a second rule five minutes later to hide all mail from the specific accountant involved [4].
What we don't know
- Who was the specific actor or group behind the campaign?
- Were any funds successfully stolen through the identified payroll fraud attempts?
- How many of the 79 organizations detected the breach independently before the Huntress report?
- Which specific users or roles were targeted within the 79 compromised organizations?
Sources
- Huntress tracks stolen-session replay into 79 Microsoft 365 organizations without a password — Start with Identity, Oct 22, 2026
- Hackers Hijack Microsoft 365 Sessions and Replace Victims' MFA Methods to Maintain Access — cyberpress.org
- Microsoft 365 accounts compromised at 79 organizations, no passwords needed - Help Net Security — helpnetsecurity.com
- Legitimate entry with the right key—MFA-passed tokens and emptied inboxes|白梟と226人の眷族 — note.com
Photos and video from the reports
- Photo: Overall statistics of the M365 token spray and replay campaign observed by Huntress.
- Video: A blog post from Start with Identity detailing Huntress's tracking of stolen-session replay.
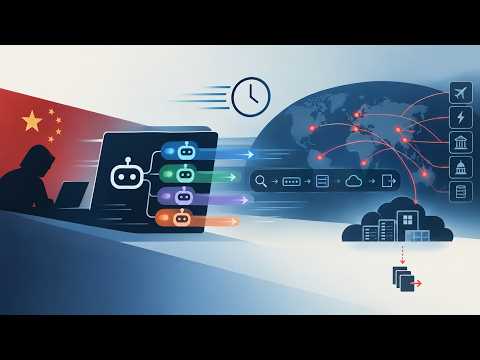
- Photo: An illustration depicting the hijacking of Microsoft 365 sessions to bypass MFA.
- Video: A video discussing token theft and disrupting the cyber attack kill chain.
Further reading
- Identity-First Security: How to Defend Against Cloud Breaches
Detailed guidance on aligning Zero Trust and phishing-resistant MFA with CISA standards to prevent cloud breaches.
- The Identity Breach You Didn't Know You Had: Google Workspace
A report on how session hijacking and device code phishing are used to compromise Google Workspace accounts.