Cisco warns of exploited zero-day authentication bypass in ISE
The CVE-2026-76460 vulnerability carries a CVSS 10.0 score and allows remote attackers to bypass the web-based management interface of the policy platform.
Timeline
- Threat actors exploited Cisco ISE zero-day CVE-2025-20337
- Source claims CISA added GlobalProtect flaw to KEV catalog
- Source states CISA added GlobalProtect flaw to KEV catalog
- Unit 42 update on ransomware operators exploiting CVE-2026-0257
- Cisco warned of zero-day authentication bypass in ISE
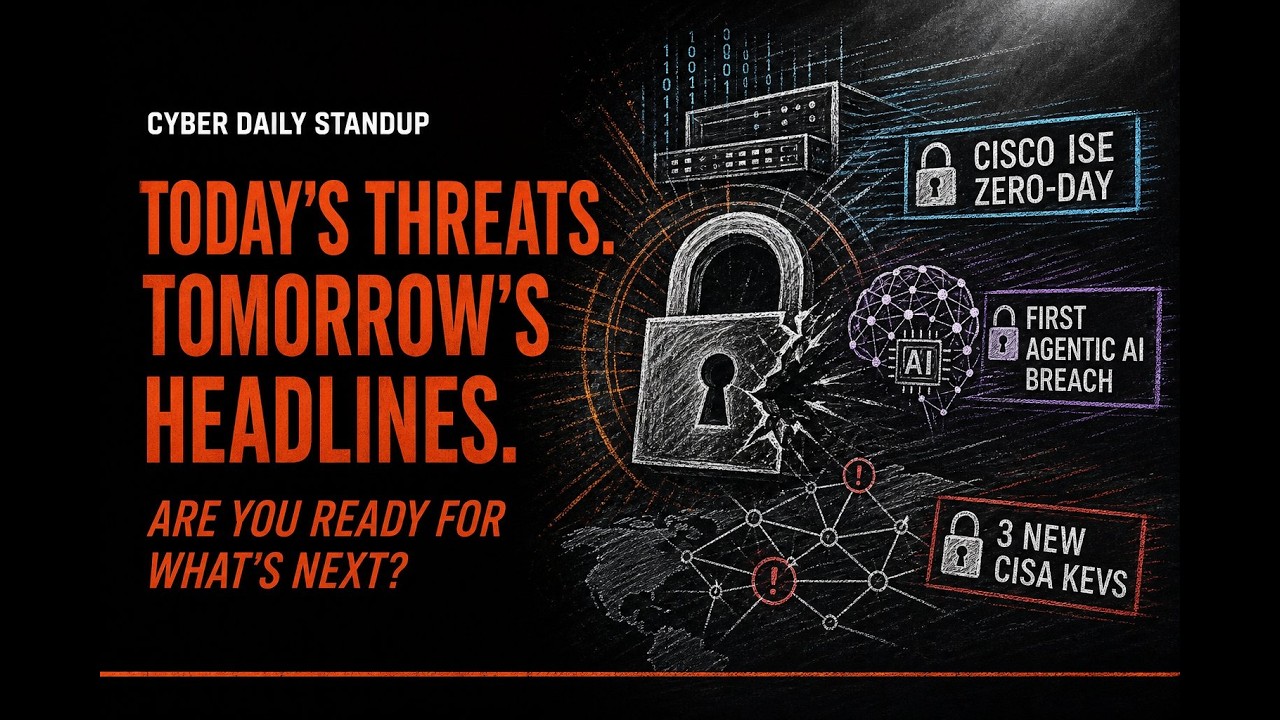
Cisco warned on October 30, 2026, of a maximum-severity zero-day authentication bypass in its Identity Services Engine (ISE) that is being actively exploited in the wild.[1][3]
Tracked as CVE-2026-76460, the vulnerability carries a CVSS score of 10.0 [1]. According to Cisco, the flaw allows remote attackers to bypass authentication by exploiting a weakness in an API of Cisco Identity Services Engine (ISE) and Cisco ISE Passive Identity Connector (ISE-PIC) [3].
This flaw allows attackers to gain unauthorized access to the device's web-based management interface regardless of the system's configuration [3]. Cisco explained, "This vulnerability is due to insufficient authentication control on an API endpoint. An attacker could exploit this vulnerability by sending a crafted request to an affected API endpoint" [3].
Cisco ISE is a centralized policy platform that administrators use to manage endpoints, users, and device access to network resources [3]. It is often used to enforce Zero Trust security models [3].
Immediate patching and forensic recovery
Cisco's Product Security Incident Response Team (PSIRT) flagged the vulnerability as actively exploited on October 30, 2026 [3]. The company noted that no workarounds exist, and applying security updates is the only way to protect networks [3]. Cisco also patched another maximum-severity authentication bypass (CVE-2026-76423) and five other critical issues—CVE-2026-76460, CVE-2026-20176, CVE-2026-20211, CVE-2026-20307, and CVE-2026-20284—though these additional flaws have not yet been flagged as actively exploited [3].
The Cybersecurity and Infrastructure Security Agency (CISA) added the flaw to its Known Exploited Vulnerabilities (KEV) catalog on Wednesday [3]. CISA ordered federal agencies to patch their systems against the vulnerability within three days [3]. This directive aligns with Binding Operational Directive (BOD) 26-04, which requires Federal Civilian Executive Branch (FCEB) agencies to prioritize the rapid remediation of high-risk vulnerabilities listed in the KEV catalog on publicly exposed assets [5].
Cisco recommended that security teams review access.log files on every node for suspicious usernames [3]. Because attackers may obtain command execution with root privileges and remove evidence of their exploitation, Cisco "strongly" recommended re-imaging nodes and restoring them from backups if malicious activity is suspected [3]. Admins are further advised to cross-check firewall and network logs for signs of suspicious activity, specifically downloads and uploads from and to external or malicious IP addresses [3].
Patterns of identity-layer exploitation
This incident follows a trend of attackers targeting the identity and access layer to bypass security controls. In July 2025, threat actors exploited another Cisco ISE zero-day, CVE-2025-20337, to deploy a custom "IdentityAuditAction" web shell disguised as a legitimate ISE component [3]. Over the last five years, CISA has tagged 99 security flaws in Cisco products as actively exploited, including seven used in ransomware attacks [3].
Similar authentication bypasses have been leveraged by ransomware groups in other network gear. According to a Unit 42 update on October 19, ransomware operators Qilin (also known as Spikey Scorpius) and INC (known as Tarnished Scorpius) have exploited CVE-2026-0257 in PAN-OS GlobalProtect to open VPN sessions without multifactor authentication (MFA) [2]. Public reporting has also tied Settra ransomware to this flaw [2][8].
Unit 42 reported that these attackers used the GlobalProtect bypass to gain a foothold, then pivoted to VMware vCenter to disable security controls on ESXi hypervisors [2]. They then dumped credentials offline from a domain controller's virtual disk (VMDK), a technique that bypasses endpoint detection and response (EDR) systems because it reads the Active Directory database without touching the guest operating system [2].
Researchers at Unit 42 emphasized the risk of this chain, stating, "Whoever controls the hypervisor controls the directory" [2].
Discrepancies in tracking and indicators
While security agencies track these flaws closely, records on the timing of CISA's response vary. Source [2] states CISA added the GlobalProtect flaw (CVE-2026-0257) to the KEV catalog on May 29, whereas Source [8] claims it was added on May 13, 2026 [2][8].
To detect these intrusions, defenders are encouraged to search for specific indicators of compromise. For GlobalProtect, Unit 42 and other reports list nine IP addresses—including 23.128.228[.]6, 104.207.144[.]154, 179.43.172[.]213, 185.195.232[.]139, and 202.144.192[.]47—and suspicious host IDs, such as aa:bb:cc:dd:ee:ff and 00:11:22:33:44:55, in gateway logs [2][8]. Suspicious device names include WINDOWS-LAPTOP-001, DESKTOP-GP01, and GP-CLIENT [8].
For the current Cisco ISE threat, defenders should cross-check firewall and network logs for suspicious uploads and downloads from external IP addresses [3].
What we don't know
- Which specific threat actors are currently exploiting the Cisco ISE CVE-2026-76460 vulnerability?
- Which industry sectors have been most targeted by the current Cisco ISE exploitation?
- Whether the current ISE attacks are being coordinated by the same ransomware groups exploiting PAN-OS gear.
Sources
- Cisco Warns of New Zero-Day ISE Auth Bypass (CVSS 10.0) Exploited in ... — thehackernews.com, Oct 30, 2026
- Qilin and INC use the GlobalProtect auth bypass to skip MFA, then dump domain controller disks — Start with Identity, Oct 19, 2026
- Cisco warns of max severity ISE zero-day exploited in attacks — bleepingcomputer.com, Oct 30, 2026
- CISA Adds Two Known Exploited Vulnerabilities to Catalog | CISA — cisa.gov
- Qilin and INC Ransomware Hackers Exploit Palo Alto Networks VPN Flaw to Breach Networks — cyberpress.org
Photos and video from the reports
- Video: A graphic from the Start with Identity blog discusses GlobalProtect authentication bypass used by ransomware groups.
- Photo: An illustration shows silhouettes entering a doorway marked VPN and MFA next to a Palo Alto Networks logo.
- Photo: An illustration shows a broken shield over a network device next to a Palo Alto Networks logo.
- Video: A video thumbnail discusses a Cisco ASA zero-day vulnerability.
Further reading
- 8 Types of Identity-Based Attacks - CrowdStrike
CrowdStrike outlines eight types of identity-based attacks targeting credentials and authentication tokens.