SonicWall warns of SSLVPN flaw that bypasses MFA
SonicWall urges prompt upgrades to fix a vulnerability potentially exploited in the wild, while CERT/CC discloses separate flaws in Logto authentication.
SonicOS SSLVPN vulnerabilities
SonicWall has warned customers to patch a SonicOS SSLVPN vulnerability that could allow attackers to bypass multi-factor authentication (MFA) and SAML authentication checks [1].
The flaw, tracked as CVE-2026-19868, carries a CVSS score of 7.1 [1].
This issue specifically affects SSLVPN when SAML is enabled for logins [1]. To exploit the flaw, an attacker must possess valid credentials for an alternate authentication method [1]. These credentials may allow access without passing the SAML controls designed to protect the connection [1].
Successful exploitation may skip MFA enforced through SAML [1].
SonicWall investigated a report indicating potential exploitation and strongly urges customers to upgrade promptly [1]. The company's November 6 security advisory lists this as one of seven issues [1].
Other vulnerabilities in the advisory include:
- CVE-2026-107155 and CVE-2026-107154: Both score 8.8 and affect the management interface [1].
- CVE-2026-82308: A pre-authentication heap buffer overflow in SSLVPN rated 7.5 [1].
- CVE-2026-77708 and CVE-2026-77709: Both score 5.9 and affect the TACACS+ authentication client, potentially causing application-level denial of service [1].
- CVE-2026-19703: Rated 5.2, this could expose a limited platform credential on virtual appliances to an attacker with local access [1].
Affected SonicOS versions
The vulnerabilities affect Gen7 hardware and NSv appliances running SonicOS 7.3.3-7015 or earlier, and Gen8 hardware and NSv appliances running 8.2.2-8015 or earlier [1].
SonicWall provides fixes in 7.3.4-7013 and later for Gen7, and 8.2.3-8015 and later for Gen8 [1]. No workaround is listed [1].
Logto authentication flaws
CERT/CC disclosed six vulnerabilities in Logto [6].
Two of these flaws, CVE-2026-15611 and CVE-2026-15616, enable attackers to skip MFA and bypass single sign-on (SSO) authentication [6].
Passkey adoption trends
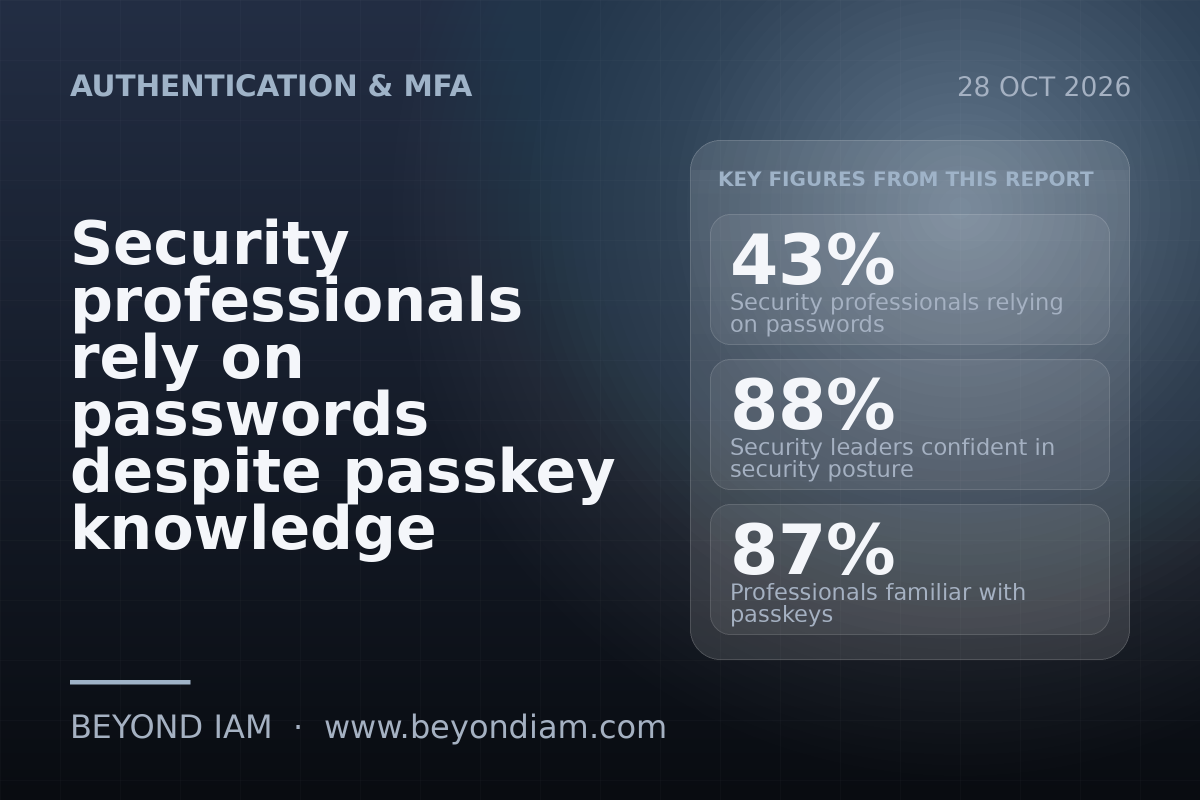
A 2024 Online Authentication Barometer study by the FIDO Alliance found that 57% of consumers are now aware of passkeys, up from 39% in 2022 [4].
The study, conducted across 10 countries, noted high adoption rates in China and India, followed by Japan and the UK [4].
FIDO (Fast IDentity Online) is a certification for authentication protocols aimed at eliminating passwords [4]. Passkeys use public and private key cryptography to enable seamless logins [4].
The FIDO Alliance is an open industry association formed in 2012 [4]. Its members include more than 250 organizations, including Apple, Google, Microsoft, Amazon, Bank of America, Target, CVS Health, and SK Telecom [4], [7].
What we don't know
- Whether any active exploits have been confirmed for the Logto vulnerabilities [6].
- The identity of the attackers, specific victims, or the scale of activity regarding the SonicWall SSLVPN exploitation report [1].
- Which specific demographic groups in the FIDO study experienced the highest rates of cart abandonment due to password frustration [4].
Sources
- [1] SonicWall Warns of Potential In-the-Wild Exploitation of SSLVPN Flaw That Bypasses MFA — cybersecuritynews.com, Nov 7, 2026
- [4] What is FIDO? What is FIDO Alliance? FIDO Authentication Explained — passkeys.com, Nov 7, 2026
- [6] Logto Vulnerabilities Allow SSO Authentication Bypass — securityonline.info, Nov 8, 2026
- [7] Passing on Passwords - Communications of the ACM — cacm.acm.org, Nov 8, 2026